From stolen data and malware services to international scam centres, cybercrime has grown into a connected global threat. But what does the trillion-dollar estimate really measure—and who pays the price?
Cybercrime is often pictured as a hacker breaking into a computer, stealing information and disappearing. The reality can be far more organized.
Some criminal operations involve developers who create malware, sellers who trade stolen information, operators who gain access to company systems, fraudsters who contact victims and intermediaries who move the money. Different people can handle different parts of the same operation, sometimes across several countries.
From Early Computer Misuse to a Global Cybercrime Economy
Cybercrime did not begin with today’s internet. Its history developed alongside computer systems, communications networks and the growing ability to access information remotely.
Before the modern internet
Computer security concerns emerged as organisations increasingly relied on mainframes and shared computing systems. Telephone-network enthusiasts also explored ways to manipulate signalling systems, a practice known as phone phreaking. These developments are important precursors, but they were not all the same kind of crime.
Early systems and communicationsComputers become interconnected
As computer networks expanded, unauthorised access and malicious software could affect systems beyond a single machine. Security weaknesses in networked computers became a growing concern, setting the stage for incidents that could spread between connected organisations.
Networked computer misuseThe Morris Worm disrupts the early internet
A program released from an MIT computer spread rapidly across connected Unix systems. The FBI estimates that around 6,000 of the approximately 60,000 computers then connected to the internet were affected within 24 hours. It did not destroy files, but it slowed systems and disrupted university and research operations.
The incident became a landmark in internet security. Its author was convicted in 1990 under the US Computer Fraud and Abuse Act.
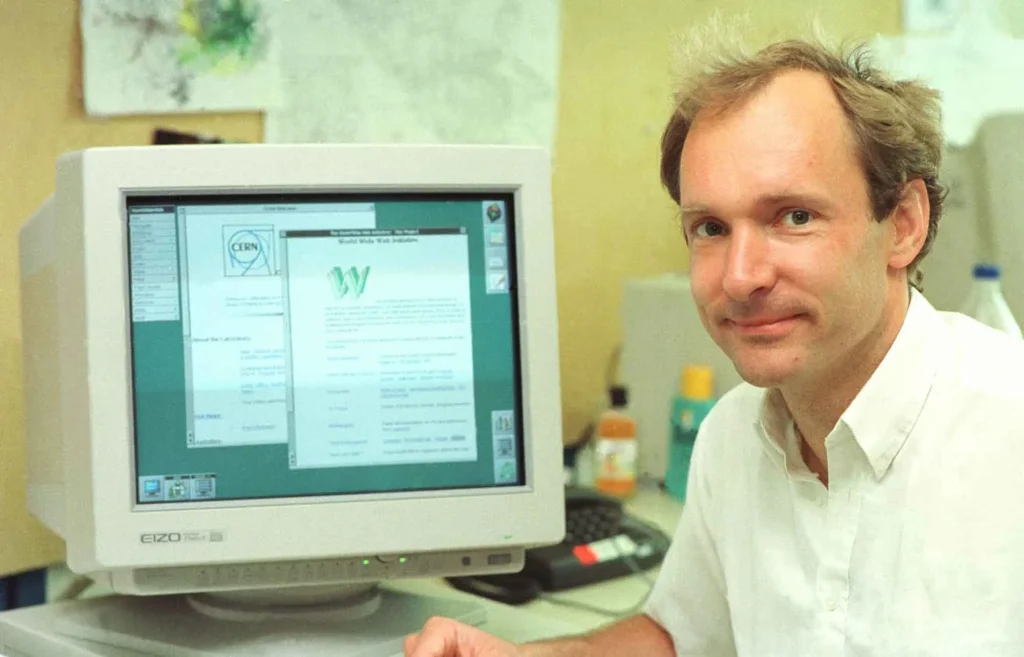
The World Wide Web expands
The Web made online information and communication increasingly accessible. As websites and internet use grew, opportunities for online deception, unauthorised access and other forms of digital abuse grew alongside legitimate uses of the technology.
The Web itself was created to support information-sharing. Its development should not be confused with the origin of cybercrime.
Explore the Web’s history at CERNOnline fraud and malware become scalable
Wider internet access, online banking and digital commerce created new opportunities for criminals to target people and organisations remotely. Phishing, credential theft, botnets, ransomware and data breaches became major parts of the modern threat landscape.
Cybercrime increasingly crossed borders, making investigations and the recovery of stolen money more complicated.
Fraud, malware and stolen dataA connected global criminal economy
Modern cybercrime can involve malware developers, stolen-data sellers, access brokers, fraud operators and people who move criminal proceeds. Some sell tools or services to other criminals rather than carrying out every stage of an attack themselves.
International scam operations and coercive scam centres also show that the harm extends beyond financial losses to include exploitation and human trafficking.
Services, specialisation and global reach
Cybercrime has no single starting point. Its modern form developed as computers, networks and online services expanded—and as criminals found new ways to exploit them. The scale of today’s problem is the result of that long evolution, not one isolated event.
Cybersecurity Ventures estimated that cybercrime would cost the world US$10.5 trillion in 2025 and projected a figure of US$10.8 trillion for 2026. These are industry estimates of broad economic damage, not audited totals of money stolen or income received by criminals.
That distinction is essential. The size of the estimated damage is striking, but the bigger story is how cybercrime operates, how it affects ordinary people and businesses, and why the international response is so difficult.
THE GLOBAL PICTURE
The scale of cybercrime
One global estimate. Two national reporting snapshots. These figures measure different things.

Cybersecurity Ventures’ estimate of broad economic damage associated with cybercrime.
A forecast, not a verified total of money stolen or criminal revenue.
Losses reported in complaints to the FBI’s Internet Crime Complaint Center.
Payment fraud losses reported by UK Finance. This is not all cybercrime.
Important: these figures are not directly comparable. The global figures are industry estimates; the US and UK figures cover specific reported losses and categories.
What does the $10.5 trillion figure actually mean?
The estimate comes from Cybersecurity Ventures, a cybersecurity research and industry publication. Its definition of cybercrime costs includes stolen money, damaged data, lost productivity, intellectual-property theft, business disruption, investigation and recovery expenses, legal costs and reputational harm.
Imagine a company loses £100,000 after criminals compromise its systems. That is only part of the possible damage. The company may also need to investigate the incident, restore its systems, notify customers, pay legal fees and deal with lost business while services are unavailable.
The total cost can therefore be much greater than the amount stolen.
But there is a limitation: the US$10.5 trillion figure is a forecast, not a global audit. There is no complete, universally accepted accounting system that measures every cybercrime, every victim’s losses and every resulting business cost worldwide. Different studies may also define cybercrime and economic damage differently.
For that reason, it would be misleading to say that cybercriminals collectively earn US$10.5 trillion every year. The estimate describes the potential economic burden associated with cybercrime, not a verified criminal revenue figure.
The important question is not just how large the number is, but what lies behind it.
What do the reported losses tell us?
Although no single figure captures the full global impact, official reports show that the losses reported in individual countries are already substantial.
The FBI’s 2025 Internet Crime Report, released in 2026, recorded 1,008,597 complaints and nearly US$21 billion in reported losses from cyber-enabled crime in the United States. The FBI also recorded more than US$17.7 billion in reported losses from cyber-enabled fraud. Cryptocurrency-related complaints accounted for more than US$11 billion in reported losses, although that category overlaps with the wider figures and must not be added to them. Source: FBI, 2025 Internet Crime Report announcement.
The figures are based on complaints submitted to the FBI. They do not represent every crime committed in the United States, and they should not be mistaken for a complete national total.
Reported cybercrime losses in the US and UK
Official figures reveal substantial losses, but each country measures different types of crime.
Complaints recorded
Lost through payment fraud
The FBI also reported more than US$17.7 billion in cyber-enabled fraud losses and over US$11 billion in cryptocurrency-related complaint losses. These categories overlap with wider totals. They should not be added together, and the US and UK figures are not directly comparable.
Reported figures reflect the scope and methods of each source. They do not capture every crime or every loss.
The UK has its own measure of the financial impact. UK Finance reported that criminals stole £1.28 billion through payment fraud in 2025, a four per cent increase on the previous year. Its report covers authorised and unauthorised payment fraud, rather than every form of cybercrime. Source: UK Finance, Annual Fraud Report 2026.
These figures cannot be added together or compared directly with the US$10.5 trillion estimate. They cover different countries, categories and methods of measurement.
They do, however, show why it is important to look beyond a single global estimate. The losses recorded by authorities provide concrete evidence of the harm experienced by victims, even though the full scale of cybercrime remains difficult to calculate.
How cybercrime became a service industry
BEHIND THE ATTACK
A criminal operation can have many links
Different people may handle different stages. One group can supply the tools or access another group uses.
Build or steal
Malware is developed, or passwords and other data are stolen.
Sell or supply
Tools, stolen data or access may be offered to other criminals.
Target victims
Operators use the tools or access to attempt fraud or other attacks.
Move the proceeds
Other participants may help transfer or conceal criminal proceeds.

Why this matters: the person who contacts a victim may not be the person who created the tool, stole the data or controlled the original access. Investigations may need to uncover several connected participants.
One major change is that criminals do not always need to build every tool or carry out every stage of an attack themselves.
Europol’s 2025 Internet Organised Crime Threat Assessment describes how criminal networks trade stolen credentials, compromised accounts, access to corporate systems and other data. Information stolen in one attack can become a resource for another criminal group. Source: Europol, Steal, deal and repeat.
This is often called crime-as-a-service. It is not one single organisation, and it does not describe every cybercrime. It is a model in which specialised people or groups provide tools, access or services that others can use to commit offences.
A simplified example looks like this:
- One group develops malware or steals login details.
- Another group sells the stolen information or access to a target.
- A separate operator uses that access to commit fraud, steal data or disrupt systems.
- Other participants may help conceal or move the proceeds.
The people involved may operate in different countries and may never meet face to face. Some specialise in technical work, while others focus on persuading victims, exploiting access or handling money.
This division of labour can lower the technical barrier for some criminals. It also creates problems for investigators: arresting one participant does not necessarily reveal everyone else involved or shut down the services that supported the attack.
Cybercrime can therefore resemble a supply chain—but one designed to exploit people, businesses and digital systems rather than provide a legitimate service.
Scam centres: the human cost behind online fraud
Some of the most troubling examples of organised online fraud involve scam centres, including compounds in parts of Southeast Asia. Criminal groups have used these operations to run investment scams, romance fraud and other schemes aimed at victims around the world.
The people inside these compounds are not all in the same position. Some may be willing participants, while others have been deceived by fake job offers, trafficked across borders and forced to carry out scams under threats or abuse.
INTERPOL reported in June 2025 that people from 66 countries had been trafficked into online scam centres as of March that year. Its subsequent global financial fraud assessment reported that the nationalities of trafficked victims had expanded to nearly 80 by late 2025. The figures reflect the information available to investigators, not a complete count of every person held in every compound. Sources: INTERPOL’s June 2025 update and INTERPOL’s Global Financial Fraud Threat Assessment.
 THE HUMAN COST
INTERPOL FINDINGS
Scam centres can create victims on both sides
People from 66 countries had been trafficked into online scam centres by March 2025, according to INTERPOL.
INTERPOL’s later assessment reported that trafficked victims spanned nearly 80 nationalities by late 2025.
People who lose money
Targets may be deceived through investment, romance or other scams.
People forced to scam
Some workers are recruited deceptively, trafficked and coerced.
These figures reflect information available to investigators. They are not a complete count of every person affected. Not everyone found in a scam centre is necessarily a willing participant.
Read INTERPOL’s June 2025 update ↗This creates two groups of victims: people who lose money to online fraud and people who are trafficked and coerced into carrying it out.
That distinction matters. Someone found working inside a scam compound should not automatically be described as an organiser or a willing criminal. Investigators must establish the person’s role and circumstances.
The international nature of these operations makes enforcement harder. Victims, recruiters, financial intermediaries, digital infrastructure and suspected organisers may all be in different jurisdictions. Cooperation between police, prosecutors and financial investigators can be essential to tracing the network and its money.
What a real malware investigation reveals
In May 2025, the US Department of Justice announced charges against 16 defendants in connection with the DanaBot malware scheme. Authorities alleged that the operation had infected more than 300,000 computers worldwide, facilitated fraud and ransomware, and caused at least US$50 million in damage. These were allegations announced in connection with criminal charges, not proof that every defendant had been convicted. Source: US Department of Justice, DanaBot case.
DanaBot illustrates how a single malware operation can affect victims on a large scale. The Department of Justice said the malware could steal information, capture account credentials and provide remote access to infected computers. It had also been used as an initial means of infection for other malware, including ransomware.
The case helps explain why cybercrime is not always the work of one person sitting behind a laptop. Malware development, distribution, access to victims’ computers and the later use of stolen information can involve different participants.
It also illustrates the difference between a technical incident and its wider consequences. An infected computer may expose personal data, lead to financial fraud or become part of a larger operation. The resulting harm depends on what criminals do with that access and how victims are affected.
INSIDE A REAL INVESTIGATION
The DanaBot malware case
US Department of Justice · 22 May 2025

Why the case matters
Authorities alleged that DanaBot could steal data and account credentials, provide remote access to infected computers and facilitate fraud and ransomware.
The case shows how one malware operation can affect many computers and support several kinds of criminal activity.
Legal note: these figures describe allegations in the May 2025 announcement. Charges are not proof of guilt, and the figures should not be treated as a final court finding.
Read the US Department of Justice announcement ↗Is cybercrime becoming harder to stop?
There is no simple yes-or-no answer. Law enforcement agencies continue to disrupt criminal infrastructure, seize assets and prosecute suspects. But some criminal networks can replace tools, change suppliers or move activities when an operation is exposed.
The service-based model can make this more difficult. If one group sells access to many other criminals, removing a single fraud operation may not eliminate the original source of stolen data or access.
Cross-border investigations add another challenge. Evidence may be stored in one country, a victim may live in another, and a suspect or financial intermediary may be somewhere else. Different legal systems, reporting procedures and investigative priorities can slow a case.
Cooperation is improving in some areas. In September 2026, the US Department of Justice announced a joint arrangement with the UK’s Crown Prosecution Service and National Crime Agency to coordinate work against international scam centres and cyber-enabled investment fraud. The announcement reflects an effort to tackle the networks behind fraud, rather than focusing only on individual incidents. Source: US Department of Justice, US–UK scam-centre alliance.
But the existence of a joint investigation does not mean the wider problem has been solved. Disrupting criminal operations requires evidence, international cooperation, financial tracing and, where possible, support for the people harmed.
What can people and businesses do?
The global scale of cybercrime can make the problem feel distant and impossible to influence. In practice, a few measures can reduce the opportunities available to criminals.
What can people and businesses do?
Simple security habits cannot stop every attack, but they can make common scams harder to carry out and help limit the damage.
For individuals
Protect your accounts, devices and money.
-
Use unique passwords
Use a password manager, especially for email, banking and administrator accounts.
-
Enable multifactor authentication
Add another verification step wherever the service supports it.
-
Verify payment requests
Confirm unexpected requests using a separate, trusted contact method.
-
Update your devices
Install updates for your operating system, apps and connected devices.
-
Question urgent offers
Be wary of unsolicited investments and messages pressuring you to send money.
For businesses
Reduce exposure and prepare for disruption.
-
Restrict access
Give staff access only to the systems and information their roles require.
-
Maintain tested backups
Keep backups and regularly test that important data can be restored.
-
Prepare an incident plan
Define who responds, who must be contacted and how operations will recover.
-
Train staff to report concerns
Make it easy to report suspicious messages, account activity or payment requests.
No single measure eliminates cybercrime. These steps help reduce risk and limit potential harm.
- Use unique passwords and a password manager, especially for email, banking and administrator accounts.
- Enable multifactor authentication wherever it is available.
- Verify unexpected payment requests through a separate, trusted channel.
- Keep devices, applications and internet-connected systems updated.
- Be cautious about unsolicited investment opportunities and urgent requests for money.
- If an account may be compromised, use a trusted device to secure it, contact the relevant bank or service provider and preserve evidence.
Businesses should also limit access to sensitive systems, maintain backups that are tested regularly, prepare an incident-response plan and make sure staff know how to report suspicious activity.
None of these measures can eliminate cybercrime completely. They can reduce the risk of common attacks and help limit the damage when an incident occurs. Organisations should also have a plan for reporting incidents and restoring operations.
The bigger picture
The US$10.5 trillion estimate is striking, but it should not be mistaken for the amount criminals take home. It is an industry forecast of broad economic damage, with limitations that need to be made clear.
The evidence from official reports and investigations shows a serious problem in its own right: billions of dollars in reported losses, malware operations affecting hundreds of thousands of computers, and scam networks that cross borders and sometimes rely on the trafficking and coercion of people.
The criminal economy is not one organisation controlled from one place. It is a shifting collection of overlapping groups, services, tools and financial channels.
Understanding how those pieces fit together is more useful than repeating a trillion-dollar figure without context. The scale matters—but so do the people who lose their savings, the businesses forced to recover from attacks, and the workers trapped inside criminal operations.
Related reading: What Is Cybercrime? Meaning, Examples, Types and How to Stay Safe
Community discussion
Join the conversation
1 comment
Sign in to comment
Join the conversation with your Secritic account. Comments are available to signed-in readers.