Millions of people across the UK and around the world visited household-name websites on Monday, 16 November 2026, unaware that a trusted marketing tool running in the background had been hijacked to serve card-skimming, cryptocurrency-stealing, and iPhone-targeting malware.
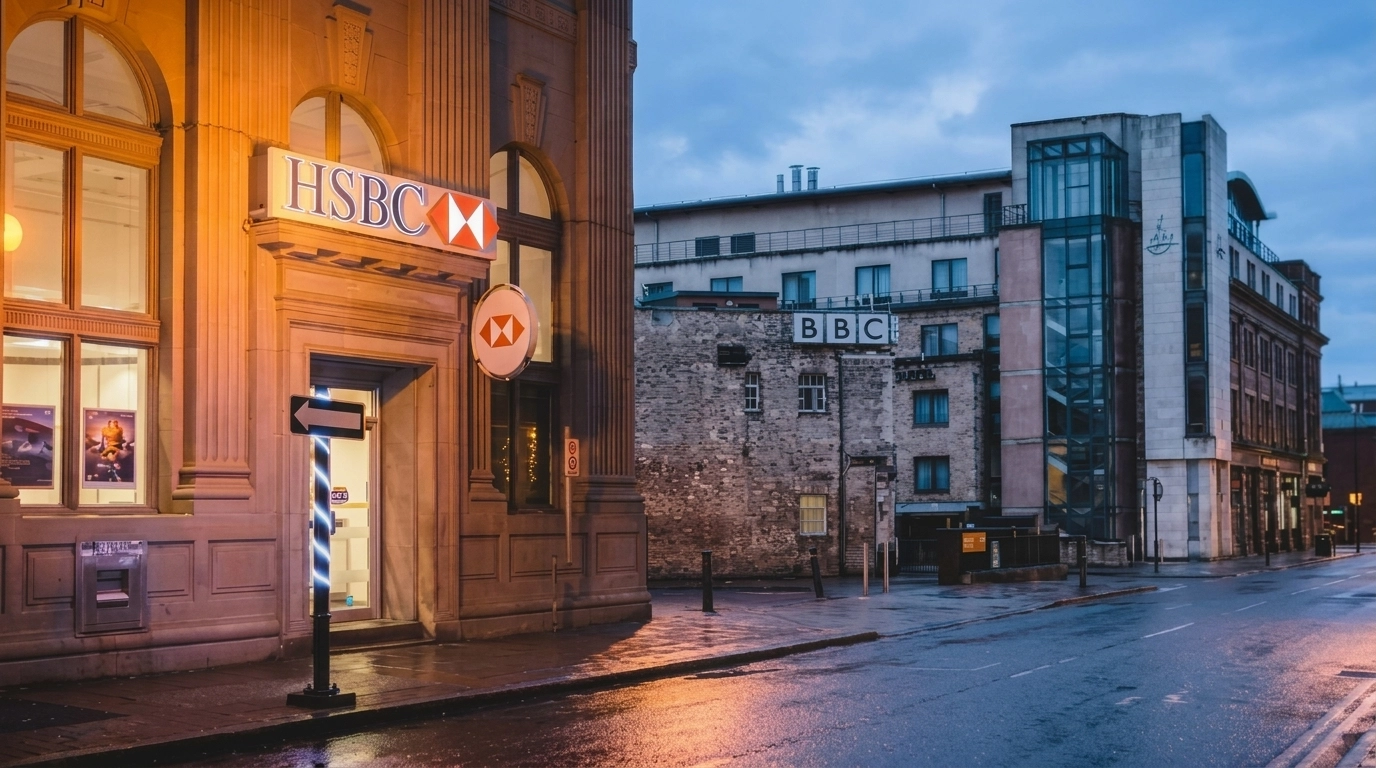
Forensic research shows that attackers exploited a vulnerability in Optimizely, a widely used website testing and personalisation platform, to inject malicious JavaScript into 188 customer scripts across 178 organisations. The affected brands include the BBC (bbc.co.uk and bbc.com), overseas and insurance portals belonging to HSBC, Virgin Media O2, TalkTalk, Zoom, CNN, Salesforce, and GitLab.
Security researchers stress an important distinction for readers. Appearing in the incident data means a website served the compromised third-party Optimizely script during the active attack window on 16 November. It does not mean the affected organisations suffered breaches of their own internal banking or editorial servers, nor that every visitor had data or money stolen.
Many large websites embed a small piece of JavaScript from Optimizely so product and marketing teams can test different page layouts or headlines. Visitors’ browsers load that file directly from Optimizely’s official content delivery network whenever a webpage opens.
According to Optimizely, intruders gained access by exploiting a flaw in how new accounts are created. In a statement to Gizmodo, Optimizely spokesperson Victoria Johnson confirmed the company “identified a security incident in which an unauthorized party exploited a vulnerability in the Experimentation account signup flow” to add “malicious JavaScript to some customer projects”. Johnson added that Optimizely “blocked access to the vulnerable path and deployed a fix” and notified all affected customers.
Using that unauthorised access, the attackers planted rogue code inside the custom Project JavaScript field of customer projects. Because browsers automatically trust scripts delivered from Optimizely’s legitimate servers, visitors’ devices executed the hidden payload without triggering standard security warnings.
As UK security researcher Scott Helme, founder of Report URI, wrote in his technical disclosure: “The important lesson here is that trusted JavaScript doesn’t always remain trustworthy. A website can be compromised through a third-party dependency without its own code or infrastructure ever being breached”.
Independent analysis by StepSecurity also showed that some sites were exposed indirectly. On GitLab’s marketing website, a third-party cookie consent tool loaded the Optimizely script, creating a multi-step supply-chain link that pulled the malicious code onto the page.
Helme first uncovered the campaign on 16 November alongside independent researcher Amirul Iman, who dubbed the operation OPTIMJACK. Helme’s scan of 1,611 Optimizely snippets identified 188 infected files belonging to 178 organisations, though he noted the true figure may be higher because his team could only test snippets discovered during the active window.
Once loaded inside a visitor’s browser, the injected code fetched an external script from 1688360.cc/track.js packed with four main functions. First, a payment-card skimmer monitored a website’s own checkout boxes for valid card numbers, expiry dates, and security codes, sending captured details to an attacker-controlled server. Payments processed inside isolated third-party checkout windows, such as Stripe or Adyen, remained out of its reach.
Second, a cryptocurrency address swapper watched open webpages and device clipboards for wallet addresses across Bitcoin, Ethereum, TRON, Solana, and several other networks, silently replacing them with addresses controlled by the attackers. Third, when the script swapped an address near payment or wallet wording, it could also capture the page address, a visual snapshot of the open page, and standard browser session cookies not locked against script access.
Fourth, visitors browsing on Apple devices were routed toward hidden frames built to deliver the Coruna and DarkSword iOS exploit kits. Further forensic review by Hudson Rock and researcher Kirk at Ohey confirmed that specimens recovered from the BBC and HSBC UAE also contained a complete embedded copy of the malware, allowing local address swapping to run even if a network firewall blocked the external command server.
Forensic timestamps show the earliest Optimizely injection appeared on the BBC snippet at 04:21 UTC on Monday, 16 November, with the track.js payload observed on bbc.com by 08:28 UTC. Later in the day, researchers captured compromised Optimizely assets tied to several overseas HSBC websites, including ://hsbc.com, hsbc.com.hk, hsbc.ae, and ://hsbc.com.sg. HSBC’s core UK retail banking website (hsbc.co.uk) did not appear in the verified dataset.
Other UK-facing brands confirmed in the dataset include Virgin Media O2, TalkTalk, Admiral, ASOS, Equifax UK, interactive investor, and IG. Helme’s crawl of 256 affected hostnames also found that 68 had no Content Security Policy configured at all, and only 24 blocked the malicious script entirely.
By roughly 21:00 UTC on 16 November, emergency cleanup was underway across major brands, including the BBC at 21:07 UTC, reducing active infections in Helme’s sample from 188 down to a single file on TalkTalk by 21:52 UTC. Early on Tuesday, 17 November, Optimizely posted an update on its status page stating: “We’ve fixed the vulnerability and removed the injected code from affected projects. We’ve also taken steps to secure affected user accounts and put additional protections in place to prevent unauthorized code from being delivered”.
In a separate notice on its official X account, Optimizely added: “Earlier today, Optimizely identified and contained a security incident affecting some Optimizely Web Experimentation customers. The vulnerable path is blocked, the injected code was removed, and customers have been contacted directly”.
As of Tuesday morning, 17 November, none of the affected UK-facing organisations had issued standalone public statements, and Cointelegraph reported that inquiries sent to affected crypto firms had not yet received replies. Neither the UK’s National Cyber Security Centre nor the Information Commissioner’s Office had announced a public advisory or investigation by Tuesday morning.
Important questions remain unanswered. While blockchain records compiled by Report URI and BleepingComputer show roughly $7,040 entering cryptocurrency wallets tied to the malware as of 19:25 UTC on 16 November, researchers caution against attributing that entire sum to Optimizely. The same threat actor ran smaller injection waves across other web tools, including Kissmetrics and StorifyMe, over the preceding days, and at least one wallet had been active since March 2026.
As Hudson Rock noted in its analysis of major news and banking portals: “That is audience context, not a count of affected visitors. The number of malicious page loads, successful thefts and compromised devices remains unknown”. Receiving an iOS exploit loader in a browser also does not prove an iPhone was compromised.
Comments inside the exploit kit’s own code state that devices running iOS 18.7.3 or later, or iOS 26.3 or later, are patched against the targeted flaws, aligning with Apple’s security release records showing those fixes shipped earlier in 2025 and February 2026. On older devices running iOS 18.6 or earlier, affected webpages reloaded every 60 seconds to retry the exploit. The identity of the attackers and the exact technical flaw inside Optimizely’s signup system remain undisclosed.
What UK Visitors Should Do Now
For most people who simply read news articles on the BBC or browsed static pages on 16 November, the practical risk of theft is low. You do not need to cancel bank cards or reset every password merely because you visited an affected site. However, anyone who entered payment card details into a website’s own checkout form, copied a cryptocurrency address, or browsed on an outdated Apple device during Monday’s exposure window should take a few proportionate precautions:
- Check bank and card statements: Review recent transactions if you entered card details directly on an affected website on 16 November, and contact your card issuer immediately if unfamiliar charges appear.
- Verify cryptocurrency wallet addresses: If you sent cryptocurrency on Monday, check your transaction history to confirm the destination address matches the intended recipient, and always verify wallet addresses on a hardware wallet screen before approving transfers.
- Update iPhones and iPads: Open Settings on your Apple device, install the latest available iOS or iPadOS update, and restart the device.
- Refresh sensitive logins: If you were logged into an affected financial or work portal during the exposure window, sign out and sign back in to replace active browser session cookies.
This is a developing story. All timelines, technical findings, and official status updates were verified as of Tuesday morning, 17 November 2026 (UTC). We have reached out to the affected UK organisations and regulators and will update this report if they comment.
Community discussion
Join the conversation
0 comments
Be the first to join in
There are no comments yet. Sign in to start a thoughtful discussion.
Sign in to comment
Join the conversation with your Secritic account. Comments are available to signed-in readers.