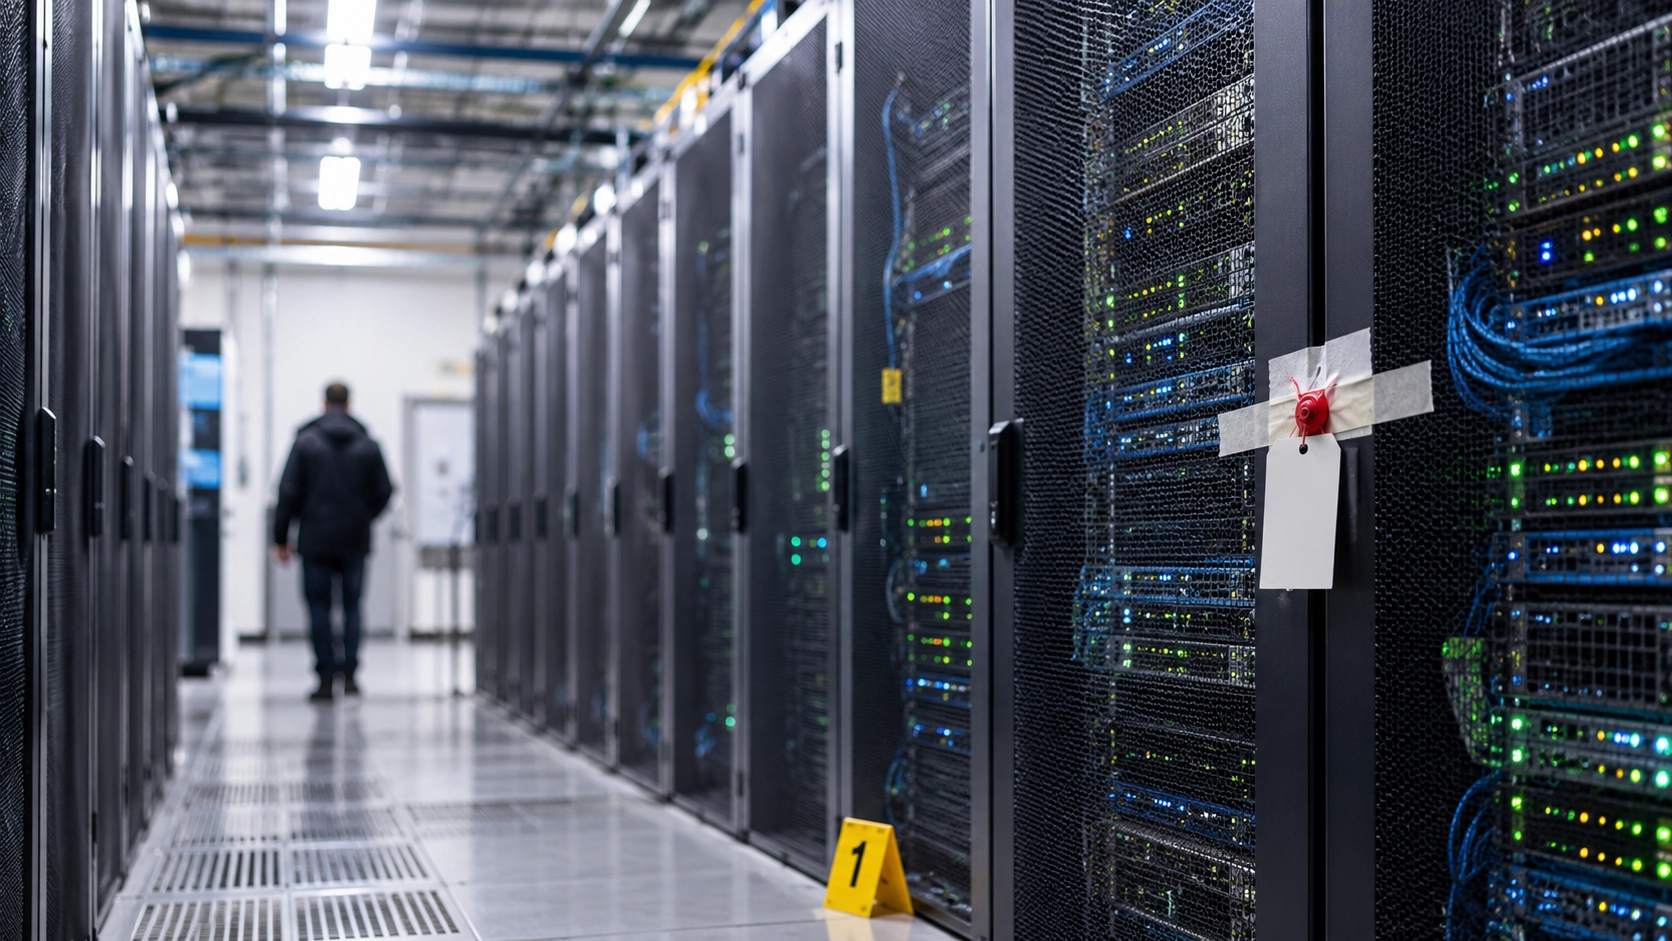
Dutch police have seized dozens of physical servers from a data centre in Limburg, taking hundreds of virtual servers offline in an international investigation into a hosting business suspected of helping cybercriminals keep their operations running.
The seizure gave investigators data and information relating to more than 3,000 customers who used the servers for criminal activities, according to Dutch police. The operation involved authorities in the Netherlands, the United States and Germany, while the UK’s National Crime Agency (NCA) assisted the US investigation.
At the centre of the case is a type of internet business known as a bulletproof hosting provider. These companies rent out servers and other internet infrastructure, but are accused of deliberately ignoring abuse complaints and law-enforcement requests so that criminal websites and services can remain online.
The US Department of Justice (DOJ) announced the court-authorised seizure of Virtualine.net on 27 October 2026. Prosecutors allege that Virtualine knowingly provided services to criminal customers and advertised a protection plan that could move their infrastructure to another company after law enforcement intervened.
The case raises a wider question: how can a business that rents out internet servers become an important part of the infrastructure behind ransomware, phishing and other cybercrime?
What happened in the international operation?
The first public announcement came from the US Department of Justice on 27 October 2026. It said authorities had seized Virtualine.net, the main website of a hosting service that also operated under the names Secury, Massgod, Spamhouse, Lanedo and Omegatech.
The seizure followed an investigation led by the FBI’s Washington Field Office. According to the DOJ, Virtualine advertised hosting and server services to customers on cybercrime forums.
On 28 October, Dutch police announced that their Midden-Nederland Cybercrime Team had seized dozens of physical servers from a data centre in the province of Limburg. The operation also took hundreds of virtual servers offline.
Dutch police said the hosting business had been linked to the facilitation of ransomware attacks, botnets, information-stealing malware, phishing and the distribution of child sexual abuse material since at least 2022. Investigators obtained data and information relating to more than 3,000 customers who had used the servers for criminal activities. Police said further investigative action against users was under way.
There is an important distinction between the two announcements. Dutch police did not name the hosting company in their statement. The DOJ identified Virtualine as the subject of its domain seizure and confirmed that the Netherlands’ Politie Midden-Nederland, Germany’s Polizei Hessen and the UK’s National Crime Agency assisted its investigation.
Cybersecurity researchers at Silent Push also identified Virtualine Technologies within the wider Omegatech network. The DOJ says Virtualine operated under the name Omegatech. This supports the connection between the investigations, but the Dutch police announcement itself does not explicitly identify the seized Limburg servers as Virtualine’s.
The distinction matters: the public evidence should not be made more definite than the authorities’ statements.
What is bulletproof hosting?
Every website, online store and internet service needs a computer system connected to the internet to make it available to visitors. Hosting companies provide that infrastructure by renting out space on physical or virtual servers.
Think of it like renting a property. A hosting company provides the space and maintains the underlying facilities. The customer uses that space to run a website or online service.
Most hosting providers have rules against criminal activity. If someone reports a website for phishing, fraud or malware, a responsible provider is expected to investigate the complaint and respond to appropriate legal requests.
A bulletproof hosting provider is different. It deliberately supplies or markets its infrastructure to criminal customers and may ignore complaints and attempts by authorities to disrupt their services.
The Australian Cyber Security Centre (ACSC) explains that these providers give cybercriminals somewhere to run websites, distribute malware and manage attacks. One provider can support many different criminal operations at the same time.
The word bulletproof is a marketing term, not a guarantee that a server cannot be identified or taken offline. The ACSC describes the term as marketing rather than genuine protection from disruption.
It is important not to confuse a bulletproof host with an ordinary hosting company that unknowingly has a criminal customer. A legitimate provider may discover that one of its customers is operating a phishing website, for example. The key difference is how the provider responds: a responsible company investigates and acts on credible reports, while a bulletproof provider is accused of deliberately allowing criminal activity to continue.
The protection plan allegedly designed to evade law enforcement
One of the most revealing details in the DOJ announcement concerns a service Virtualine allegedly advertised in March 2026.
The company called it an “additional protection plan”. According to prosecutors, customers who received an official request from law enforcement could have their criminal infrastructure moved to another company that was not formally affiliated with Virtualine. The server would then be reactivated.
Consider what that could mean in practice. If investigators contacted a hosting provider to have a phishing website taken offline, the customer could allegedly have the service moved to a different company and brought back online. The website might then continue operating from the new arrangement.
This is very different from ordinary hosting reliability. It suggests a system intended to help customers keep operating when authorities try to disrupt them.
The DOJ also cited Virtualine’s advertising on cybercrime forums. In September 2024, the provider told a user on Exploit.in that its services could be used for various illegal activities, including phishing, carding, email spam and port scanning. In June 2025, it promoted its willingness to ignore abuse complaints on HackForums.
These details are significant because they show how prosecutors say Virtualine presented its services to potential customers. They are not simply allegations based on the fact that criminal websites happened to use its servers.
How hosting infrastructure can support cybercrime
The Dutch investigation linked the hosting business to several types of cybercrime. To understand why the infrastructure matters, it helps to look at how criminals might use a server during an attack.
Ransomware
Ransomware is malicious software that can lock or encrypt a victim’s files and demand payment to restore access. Criminal groups may also use websites hosted on servers to publish stolen information or communicate with victims.
For example, after attacking a company, a ransomware group might use a website to publish samples of stolen documents and threaten to release more unless the victim pays. If the hosting provider refuses to act on abuse reports, that website may remain available for longer.
Phishing
Phishing websites imitate services that people recognise and trust, such as banks, delivery companies or email providers.
Imagine receiving a message claiming that a parcel cannot be delivered until you pay a small fee. The link opens a fake delivery website that asks for your card details. A server is needed to host that page and make it accessible to visitors.
A provider that deliberately ignores complaints can make it harder to remove such websites.
Information-stealing malware
Information-stealing malware, often called an infostealer, is designed to collect information from an infected device. This can include saved passwords, browser information and account credentials.
For example, someone might download a malicious file disguised as legitimate software. Once opened, the malware could collect information stored in the browser and send it to a server controlled by criminals. That server gives the attackers a place to receive or manage the stolen information.
Botnets
A botnet is a group of devices infected with malicious software and controlled by an attacker.
For example, criminals might infect thousands of computers, routers or other internet-connected devices. They can then send instructions to those devices through servers they control. The infected devices might be used to send spam or overwhelm a website with traffic in a distributed denial-of-service attack.
The servers used to manage these devices can therefore become important targets for investigators.
These examples help explain why a hosting provider can matter so much. It does not necessarily carry out every attack itself. Instead, it can provide the online space that allows multiple criminal operations to function.
The allegations involving explicit material and repeated warnings
The DOJ’s case also includes allegations concerning a customer identified in court records as Vendor 1.
According to prosecutors, Vendor 1 operated a criminal online forum where users could post and sell access to nude, sexually suggestive or sexually explicit images and videos involving minors and adults. The DOJ also alleges that the forum promoted a hack-for-hire service, allowing customers to pay hackers to access victims’ online accounts without permission and obtain intimate material.
Prosecutors say Virtualine began receiving notifications about sexually explicit images and videos of minors on the server in January 2026. The DOJ refers to warnings from law-enforcement agencies in Germany, Canada and Australia, the National Center for Missing and Exploited Children in the United States, and a lawyer representing a victim.
The DOJ further alleges that Virtualine continued hosting the forum despite those notices and worked with its operators to create another website where customers could upload and download material. Prosecutors said that new website was still hosted by Virtualine when the department announced the seizure and had already received at least one further abuse complaint.
These are among the most serious allegations in the case. They should be understood as claims made by US prosecutors, not as a final court finding that every allegation has been proved.
What investigators say about the money behind the service
The investigation also examined how Virtualine received payments.
According to the DOJ, the provider accepted Bitcoin through specific unhosted wallet addresses. An unhosted wallet is a cryptocurrency wallet controlled directly by its user rather than held on the user’s behalf by a centralised exchange or other service provider.
In simple terms, a customer could send Bitcoin directly to a wallet address supplied by the hosting provider instead of paying through a conventional exchange account.
That payment method does not automatically make a transaction illegal. However, prosecutors allege that Virtualine received money from criminal customers and subsequently laundered some of the proceeds to conceal their origins. The DOJ said some payments could be traced to criminal groups.
Blockchain analytics company Chainalysis, which provided intelligence support to investigators, also reported links between Virtualine’s payment addresses and ransomware operators, infostealer infrastructure, cybercrime forums, illicit shops, scams and phishing operations.
A separate analysis by blockchain intelligence firm TRM Labs provides another indication of the range of customers associated with the service. TRM reported that a Russian drug marketplace accounted for about 44% of Virtualine’s direct cryptocurrency inflows it identified, while ransomware groups accounted for about 5%.
Those figures describe TRM’s analysis of the direct payment flows it attributed to Virtualine. They are not a measure of all the money handled by the business or proof that every transaction was criminal.
The wider point is that a hosting provider can sit within a larger criminal economy. It may supply the infrastructure, receive payments from customers and have financial connections to other illicit services. Investigators can use those connections as leads when tracing how money and services move between criminal operations.
What happened to the servers and the information on more than 3,000 customers?
The figure of more than 3,000 customers is one of the most significant details in the Dutch police announcement.
By seizing the physical servers, investigators secured data and information relating to customers who used the infrastructure for criminal activities. Police said the material would be used for further investigation and that follow-up action was under way.
That does not mean more than 3,000 people have been arrested, charged or convicted. It means investigators have information that may help them examine who used the service and whether particular customers were involved in offences.
For example, if investigators find records linking a customer account to a phishing website, they may have a lead to examine. They would still need to establish who was responsible, what that person did and whether the available evidence supports further legal action.
Dutch police have not publicly itemised all the information recovered. It would therefore be premature to claim that the seizure has already identified every customer or revealed the identity of every criminal behind the services.
The physical and virtual server distinction also explains the scale of the disruption.
A physical server is an actual computer housed in a data centre. A virtual server is a separate computing environment created on that machine. One physical server can therefore run several virtual servers, each supporting a different website or online service.
Think of an office building divided into separate rented units. Each tenant operates independently, but all of them rely on the same building. If the building is taken out of use, every tenant’s space can be affected.
That is broadly what happened in Limburg: police seized dozens of physical machines, and hundreds of virtual servers running on that infrastructure went offline.
Why legitimate hosting companies can also be affected
Criminal hosting services do not always own every server or piece of network infrastructure they use.
The Australian Cyber Security Centre explains that bulletproof providers may rent or resell server space and internet addresses supplied by legitimate hosting companies, data centres or internet service providers. Those upstream businesses may not know who is ultimately using the infrastructure.
Dutch police raised a similar concern in a separate warning in March 2026. They said legitimate Dutch hosting companies could unknowingly rent server space to resellers, who then pass it on to criminal customers.
For example, a data centre might rent server capacity to a reseller that appears to be a normal business. The reseller could then rent that capacity to a customer operating a phishing service. The data centre may not initially know what the end customer is doing.
This is why the investigation should not be treated as evidence that ordinary hosting companies are generally involved in cybercrime. Dutch police have stressed that most of the country’s hosting sector takes measures against misuse.
It also explains why disrupting criminal infrastructure requires care. Taking down a shared network resource without checking who else depends on it could affect legitimate services as well.
Virtualine disputes part of the allegations
After the domain seizure, a public statement appeared in an open letter on a separate website associated with Virtualine.
The letter disputed the allegation that the provider knowingly hosted child sexual abuse material. It claimed that the company acted on reports of such material and ended its relationship with the customer identified in the DOJ announcement as Vendor 1.
The operator also asked authorities to examine the full record of notices and responses, and said the allegations should be addressed through the appropriate legal channels.
Those claims represent the provider’s response; they have not been independently established. They differ from the DOJ’s account, which alleges that Virtualine continued hosting the forum after receiving repeated notifications and helped its operators create another website.
Both accounts need to be distinguished clearly. The public announcements and the provider’s response do not amount to a final court determination of every allegation against Virtualine or the people behind it.
Does the seizure mean the entire hosting operation is offline?
Not necessarily. Taking control of a website’s domain is different from disabling every server and network used by the business.
The seizure of Virtualine.net disrupts access to the provider’s main website. The separate Dutch operation physically removed dozens of servers and took hundreds of virtual servers offline. These are related parts of the wider disruption, but they are not the same action.
Cybersecurity researchers at Silent Push reported that the wider Omegatech network was not completely offline after the domain seizure. Its analysis found that some network address ranges had very low routing visibility, which the researchers said indicated serious disruption to the operator’s infrastructure.
This matters because a criminal hosting business may use multiple domains, servers, network addresses and upstream providers. Losing one website does not automatically prove that every service has stopped working.
The Virtualine operator’s open letter also acknowledged that it could attempt to rebrand and build a new website. That statement does not establish that the business has resumed operating, but it illustrates the possibility of trying to return under another name.
The longer-term impact will depend on what investigators can establish from the seized data, whether they can identify the people behind the services and whether further action prevents the same infrastructure from reappearing elsewhere.
What this means for businesses and ordinary internet users
Most people will never knowingly rent a server from a bulletproof hosting provider. The risk is more indirect: criminal infrastructure can support websites and services used to target ordinary internet users.
A fake delivery website could steal payment details. An infostealer operation could collect passwords from an infected computer. Ransomware infrastructure could help criminals attack a business and disrupt services that its customers depend on.
For individuals, the basic precautions remain important:
- Check the website address before entering passwords or payment details, particularly when you arrive through an unexpected message.
- Avoid opening suspicious links or downloading files from untrusted sources.
- Use multi-factor authentication on important accounts, so a stolen password alone is less likely to be enough to access them.
- Keep your devices, browsers and security software updated.
Businesses have additional responsibilities. They should understand which companies supply their hosting and infrastructure, check whether those providers have clear abuse-reporting procedures, maintain independent backups and monitor systems for suspicious activity.
A professional-looking website or a low server-rental price does not, by itself, establish that a hosting provider is trustworthy.
The wider lesson from the Limburg investigation is that cybercrime does not depend only on people writing malicious software or stealing passwords. It also relies on the infrastructure that keeps criminal websites, malware systems and online services running.
Dutch police have taken dozens of physical servers and hundreds of virtual servers offline, while investigators now hold information relating to more than 3,000 customers. The next important question is what that evidence will reveal about the people and operations behind the infrastructure — and whether authorities can turn this disruption into lasting action.
Community discussion
Join the conversation
0 comments
Be the first to join in
There are no comments yet. Sign in to start a thoughtful discussion.
Sign in to comment
Join the conversation with your Secritic account. Comments are available to signed-in readers.